
Kerberos
For the past nine years, we have been transitioning our authentication backend from LDAP to Kerberos. This will allow us to enable SSO (Single Sign-On) across Windows, Linux, macOS, and web logins, while also improving security.
Password self-service reset
If your personal or shared D-PHYS account password was last changed more than about nine years ago, you will need to reset it on our account page:
If your old password already meets our password-strength requirements, you may reuse it. In any case, you still need to set either the same password or a new password on the account page:
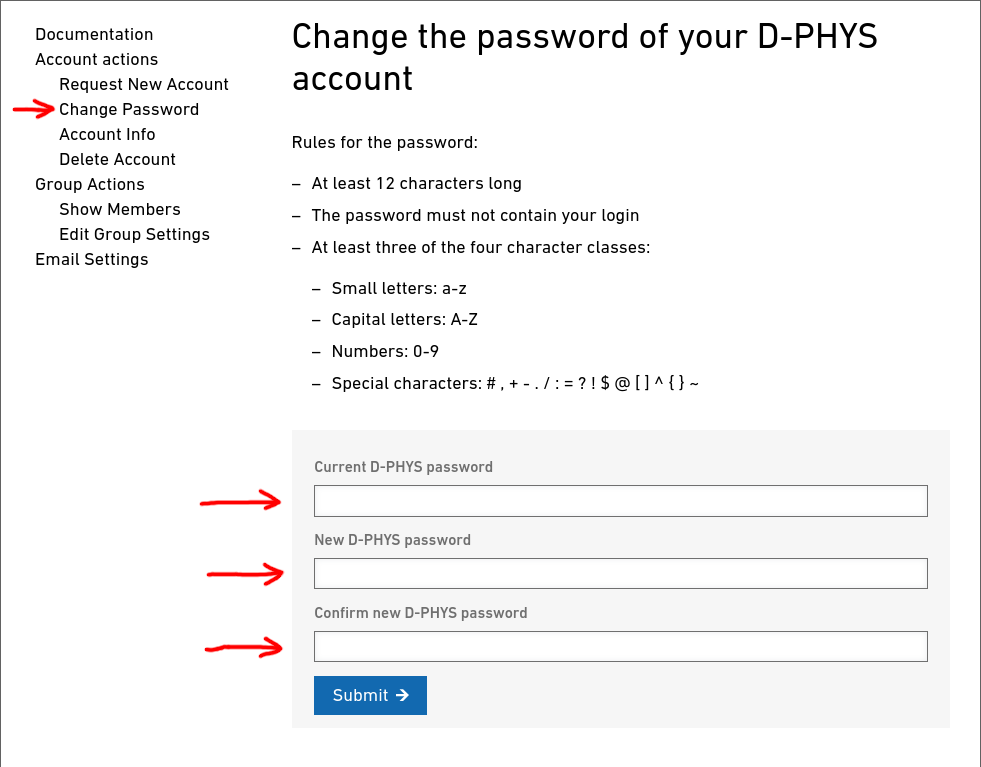
Enter your current Password in all 3 fields to keep it.
Shared accounts
If you use a shared account (for example, for group shares or email access), please coordinate the distribution of the new password within your group of users.
If you think the account is no longer needed, please contact us.
Password reset by ISG
You may have received a new password from us via Polybox:
Technical information
With the transition to our new D-PHYS LDAP servers in 2017-2018 we also started collecting authentication information in our Kerberos backend. This only happens when the password is reset or changed. Some accounts with a long and distinguished service record are still missing these additional secrets for historic reasons.
The LDAP servers will continue to serve as authentication and authorization provider, even after the full migration to Kerberos authentication in the future.